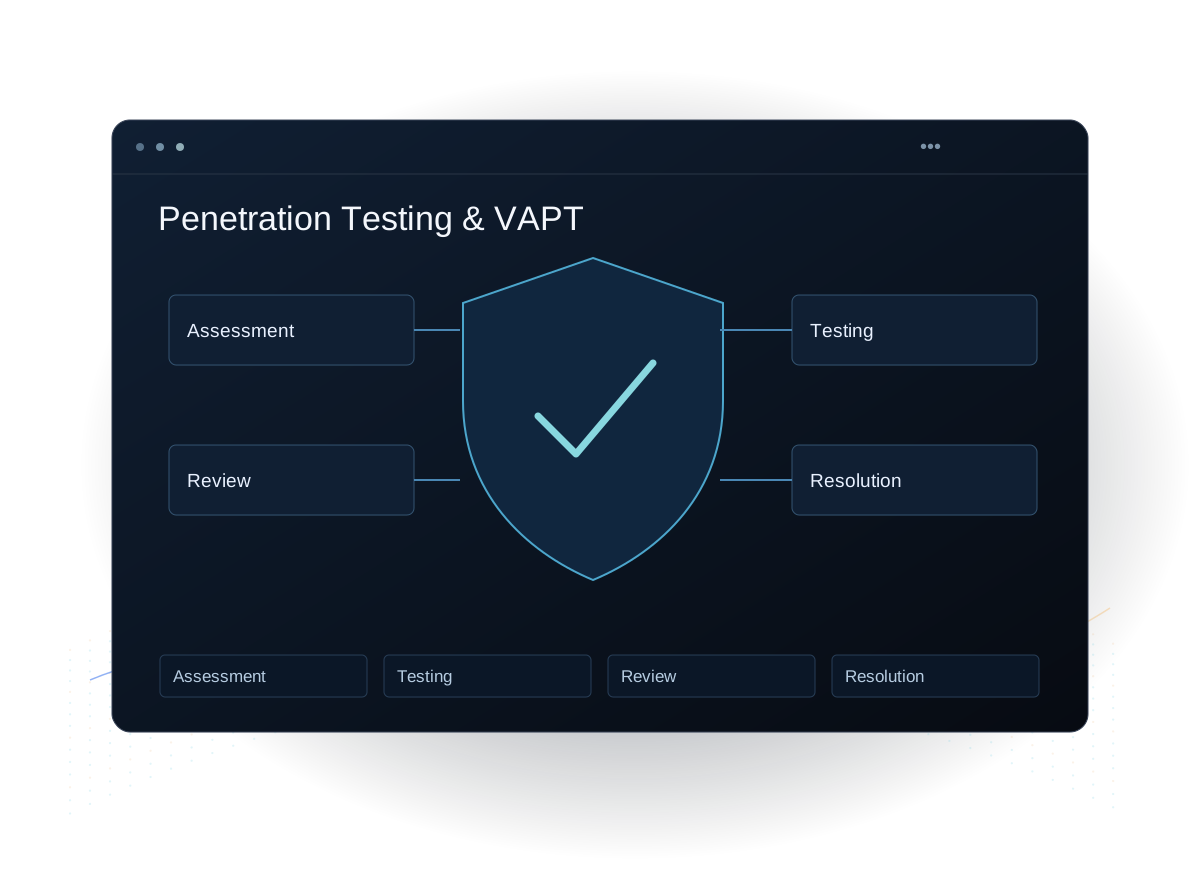
Penetration testing and VAPT for web, mobile, API and network.
Mindrops runs vulnerability assessment and penetration testing across web, mobile, API and network — combining manual testing with automation, with clear remediation guidance and a retest.
A selection of the software Mindrops has designed and engineered for clients.
Quick Commerce · Logistics
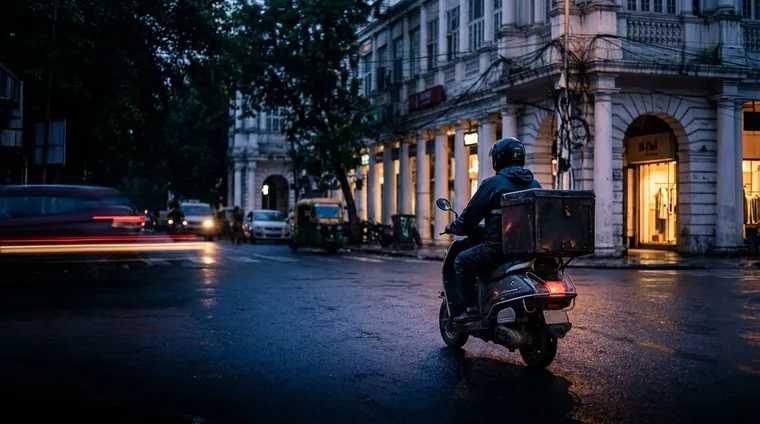
RocketZone — Rider Delivery App
A custom Android rider app with real-time order assignment, Google Maps navigation, COD collection tracking, returns and exchange pickups, and delivery proof.
Designed, built, tested and deployed between January and June 2026.
Total post offices1,65,000The largest postal network in the world
Government · GovTech
India Post — Grievance Redressal
An AI-automated platform on Mindrops’ LazyMonkey foundation that categorises, prioritises, routes and auto-responds to every grievance, with one SLA-tracked record for central and regional teams.
Awarded via GeM (Nov 2025), it auto-triages thousands of grievances a day for a network of 1.5 lakh+ post offices.
Cafés in India50+outlets across India, served by the systems we builtBrewing since 1963
AI · Food & Beverage
BeanBot — The Coffee Bean & Tea Leaf
An embeddable AI chat assistant grounded in live catalogue and store data, with an “Order Now” action on every product and a no-code admin console for content and pricing.
Live across 50+ outlets in India, handling about 10,000 conversations a month and around 50 orders a day.
Mindrops runs penetration testing and VAPT across web, mobile, API and network — combining manual and automated testing, aligned to OWASP, to find exploitable weaknesses in applications, APIs, networks and devices. Each engagement delivers prioritised remediation guidance and a retest.
01
Web app testing
Manual and automated testing against OWASP Top 10 and business-logic flaws.
02
Mobile testing
iOS and Android app testing — storage, transport, auth and API security.
03
API testing
REST and GraphQL API testing for auth, access-control and injection flaws.
04
Network & infra
External and internal network and infrastructure penetration testing.
05
Remediation guidance
Prioritised, practical fixes for each finding.
06
Report & retest
Clear reporting for stakeholders and auditors, plus a retest to confirm fixes.
When to commission a penetration test
Before a launch or major release
Product teams that want exploitable weaknesses found and fixed before real users — and real attackers — arrive.
Customer and audit requests
Organisations asked by enterprise customers, regulators or auditors for an independent penetration-test report.
After significant change
Platforms that have added APIs, integrations, cloud infrastructure or authentication flows since they were last tested.
Apps handling sensitive data
Web and mobile applications processing payments, personal data or government records, where a breach carries legal and reputational cost.
Why Mindrops for penetration testing
Manual testing after automated scans
Automated tools cover breadth; our testers then chase business-logic flaws, broken access control and chained exploits that scanners miss.
Findings developers can act on
Each finding comes with reproduction steps, impact and a specific fix, written for the engineers who will apply it.
Retest built into the plan
A retest is part of the engagement, so the final report shows which issues are confirmed closed.
Explicit, comparable coverage
Testing maps to the OWASP Top 10, OWASP MASVS for mobile and the OWASP API Security Top 10, so what was covered is clear.
Technologies we use
Standards
OWASP · OWASP MASVS · NIST
Scope
Web · Mobile · API · Network
Approach
Manual + automated · Remediation · Retest
Client reviews
Extra capacity for software and cloud
A Mindrops team working alongside the client’s own engineers on software development and cloud-based projects, brought in to add reliable delivery capacity.
From the client’s review
“Mindrops handled complex requirements with ease and added value throughout the project.”
An annual maintenance contract to stabilise an aviation recruitment website and fix its online application workflow, which has to hold up during active hiring drives.
From the client’s review
“Most aviation candidates apply through phones, and the fixes to the application flow reflected a practical understanding of that, not just surface-level design changes.”
A mobile app, website and admin dashboard connecting patients in rural and semi-urban India with doctors, with video consultations, digital prescriptions and patient registration.
From the client’s review
“The UI/UX design process was collaborative and they kept the end user in mind throughout, which mattered a lot for a platform targeting rural users.”
Vulnerability assessment finds and ranks weaknesses broadly; penetration testing actively exploits them to show real risk. VAPT combines both.
What can Mindrops test?
Web and mobile apps, REST/GraphQL APIs, and external/internal networks and infrastructure.
Does Mindrops help fix what it finds?
Yes. Mindrops delivers prioritised remediation guidance and retests after fixes to confirm the issues are closed.
Will it disrupt production?
Mindrops scopes and schedules testing to avoid disruption, and can test staging environments where appropriate.
Does a VAPT report help with compliance?
Yes. The report and retest give auditors and enterprise customers documented evidence of testing and remediation. For the wider control framework, see governance, risk & compliance.
Tell us what you want tested — web, mobile, API or network — and any deadline driving it. We will reply within one business day to scope the engagement.