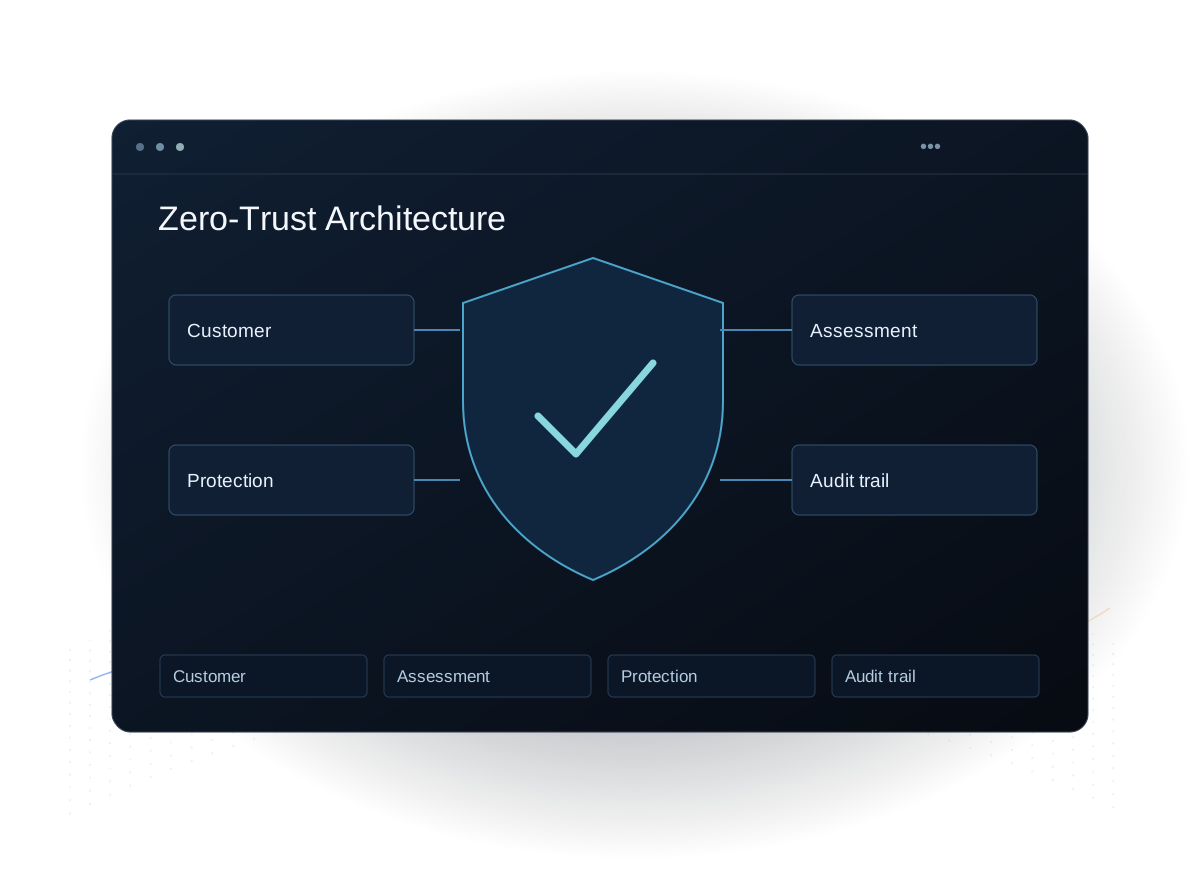
Zero-trust architecture that verifies every access request.
Mindrops designs and implements zero-trust architecture — identity-first access, least privilege, micro-segmentation and continuous verification — so a breach in one place doesn’t become a breach everywhere.
A selection of the software Mindrops has designed and engineered for clients.
SaaS · Influencer Marketing
Activate by Bloglovin'
A dedicated onshore and offshore Mindrops team built, upgraded and maintained the platform with Agile delivery — campaign matching, messaging and real-time reporting.
Maintained for 4+ years, scaling to 130,000+ influencers and 100,000+ brands on a network serving 16M+ users a month.
A custom Android rider app with real-time order assignment, Google Maps navigation, COD collection tracking, returns and exchange pickups, and delivery proof.
Designed, built, tested and deployed between January and June 2026.
Total post offices1,65,000The largest postal network in the world
Government · GovTech
India Post — Grievance Redressal
An AI-automated platform on Mindrops’ LazyMonkey foundation that categorises, prioritises, routes and auto-responds to every grievance, with one SLA-tracked record for central and regional teams.
Awarded via GeM (Nov 2025), it auto-triages thousands of grievances a day for a network of 1.5 lakh+ post offices.
Mindrops designs and implements zero-trust architecture — identity-first access, least privilege, micro-segmentation and continuous verification — across applications, cloud and infrastructure. The model trusts no user, device or network by default and verifies every access request continuously, so one breach does not become a breach everywhere.
01
Identity-first access
Strong authentication, MFA and conditional access as the new perimeter — for users and services alike.
02
Least privilege
Just-enough, just-in-time access so a compromised account can reach only what it must.
03
Micro-segmentation
Network and workload segmentation that contains blast radius and stops lateral movement.
04
Continuous verification
Every request re-evaluated on identity, device posture and context.
05
Workload & cloud
Zero-trust extended to services, APIs and cloud workloads as well as user logins.
06
Monitoring & policy
Centralised policy and telemetry so access decisions are consistent, logged and auditable.
Who we build zero-trust architecture for
Hybrid and remote workforces
Staff, contractors and partners connecting from anywhere, where VPN access grants far more reach than each person needs.
Flat networks and shared credentials
Environments where one stolen password or compromised server could move laterally across most of the estate.
Cloud and microservice estates
Services and APIs calling each other across clouds and clusters without strong service identity or authenticated, encrypted connections.
Standing third-party access
Vendors and integrators with long-lived access to production systems that is rarely reviewed or revoked.
Why Mindrops for zero-trust architecture
Sequenced for early impact
We start where risk concentrates — usually identity, MFA and privileged access — so protection improves from the first phase of the programme.
Users and workloads together
Service identity, mutual TLS and segmentation cover APIs and cloud workloads as well as employee logins.
Policies tested on real user journeys
Access policies are tested against real user journeys, so stronger verification doesn’t push staff into risky workarounds.
Auditable access decisions
Access policy is centralised and every decision logged, giving security teams and auditors one place to see who reached what, and why.
Technologies we use
Identity
SSO · MFA · Conditional access · SCIM
Network & workload
Micro-segmentation · Service mesh · mTLS
Cloud
AWS · Azure · GCP · Posture management
Standards
NIST 800-207 · OWASP
Client reviews
Extra capacity for software and cloud
A Mindrops team working alongside the client’s own engineers on software development and cloud-based projects, brought in to add reliable delivery capacity.
From the client’s review
“Mindrops handled complex requirements with ease and added value throughout the project.”
An annual maintenance contract to stabilise an aviation recruitment website and fix its online application workflow, which has to hold up during active hiring drives.
From the client’s review
“Most aviation candidates apply through phones, and the fixes to the application flow reflected a practical understanding of that, not just surface-level design changes.”
A mobile app, website and admin dashboard connecting patients in rural and semi-urban India with doctors, with video consultations, digital prescriptions and patient registration.
From the client’s review
“The UI/UX design process was collaborative and they kept the end user in mind throughout, which mattered a lot for a platform targeting rural users.”
A security model that assumes no user, device or network is trusted by default. Every access request is verified continuously on identity, device posture and context, and network location on its own grants no access.
Where does a zero-trust rollout start?
Usually with identity and access — strong authentication, MFA and least privilege — then micro-segmentation and continuous verification. Mindrops assesses the environment and sequences the highest-impact steps first.
Can zero-trust apply to cloud workloads as well as users?
Yes. Mindrops extends zero-trust to services, APIs and cloud workloads with mutual TLS, service identity and segmentation.
Does this align to a standard?
Yes. Mindrops aligns zero-trust designs to NIST SP 800-207, with access policy and logging that are auditable.